
Manage marketing assets in a private, safe, and centralized platform
When you share files and feedback by email, you lose control over who sees what. Filestage changes that with one secure space to manage approvals.
- ✓ 14-day free trial
- ✓ No credit card needed
- ✓ GDPR compliant
Trusted by professionals from top brands and agencies






Compliance and certifications

Cloud Security Alliance (CSA)

GDPR compliant

ISO 27001

SOC 2 certified
We hold SOC 2 Type II certification, confirmed through an independent audit of our security controls over time. This certification reflects our ongoing commitment to safeguarding your data by upholding industry-leading security practices.
Data infrastructure and encyrption
Our standard SLA offers a monthly uptime rate of 99.1%, while our Enterprise SLA uptime rate is 99.9%.

Cloud infrastructure

Data-in-transit

Data-at-rest

Pen tested
Enjoy a secure onboarding and sign on experience
Set a secure password in line with security best practices
Sign up and log in securely with OAuth or federated SSO
Control who sees your content by limiting access to reviewers
Choose exactly who you want to see your content
Stop stakeholders from sharing review links with teammates
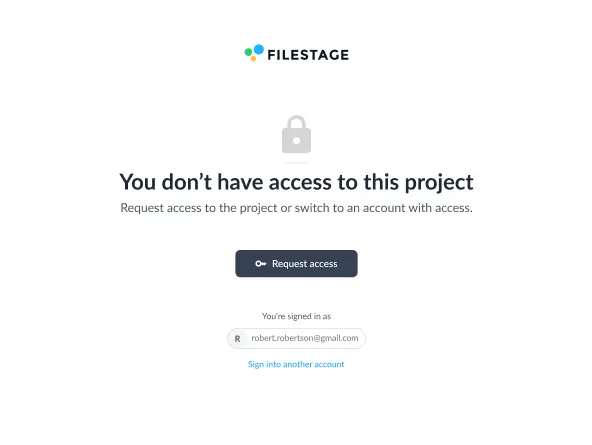

Customize access rights for team members and reviewers
Keep sensitive files secure with custom roles and permissions
Restrict actions based on your files’ review statuses
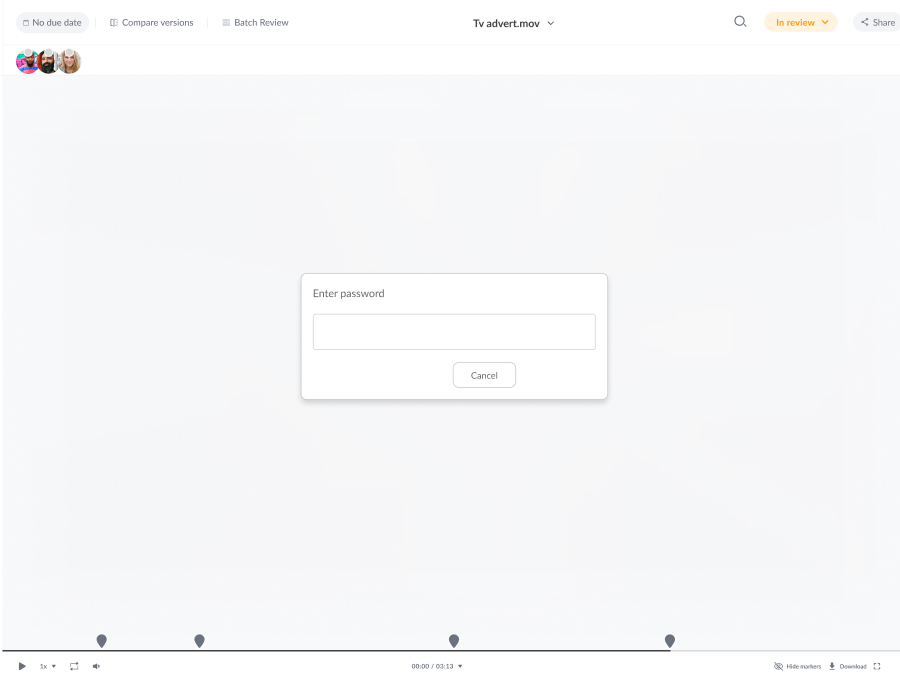
Protect your content with passwords and email verification
Make reviews extra secure by verifying users and approvals
Anonymize reviewers to protect stakeholders’ identities


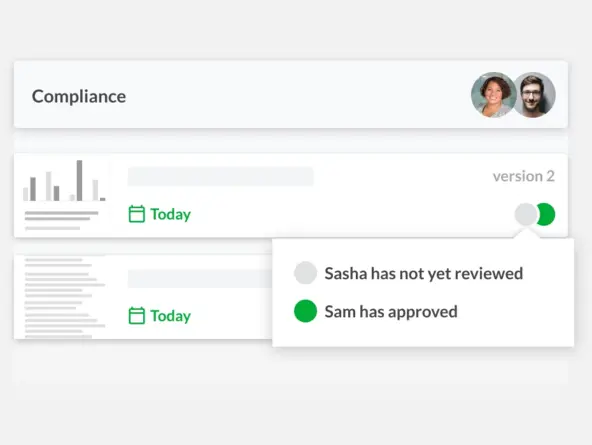
Keep a record of your review process for easy auditing and optimization
Make it easy to go back and check who approved a file
Get a log of your organization’s Filestage activity
Reach out to our customer success team for your log, or use our public API to access this data at any time.
Part of your AI content compliance stack
FAQ
Where is Filestage hosted, and where will my data be stored?
How do you manage vulnerabilities and their patches?
How do you manage changes to your platform?
How do you manage business continuity and disaster recovery?
How do you manage incidents?
We maintain an Information Privacy and Security Incident and Breach Management Policy. This is supported by a procedure for detecting and reporting incidents, assessing incidents and deciding on a course of action, responding to and recovering from the incident (i.e. implementing the decided course of action), notifying affected parties, learning from the incident, and maintaining evidence of the incident, actions taken, and lessons learned.
Does Filestage offer a Data Processing Agreement (DPA)?
We’ve incorporated our DPA into our Master Services Agreement (MSA), so you don’t have to sign it separately. But if this is a requirement from your organization, our Sales team will help.
Does Filestage make use of third parties (i.e. sub-processors)?
At Filestage, we embrace remote working. This means we’re a fully-remote and globally-distributed team that leverages third-party cloud services providers (CSPs) for our products (i.e. hosting and delivering our application, app.filestage.io). We understand that using third-party CSPs carries an element of risk. That’s why we have a robust third-party privacy and security risk management program. As part of our program, we assess each subprocessor’s privacy and security practices before using their services. This assessment includes reviewing their information security management systems and data processing agreements (DPAs). We prefer sub-processors who are GDPR-compliant and certified against industry best practice standards such as ISO 27001. In addition, and where required, we enter into DPAs with each sub-processor.


