TL;DR
- Content compliance means making sure every piece of content, from ad copy to social posts, meets legal, regulatory, brand, and accessibility standards before it publishes.
- For marketing teams, it’s the difference between shipping content fast and shipping content that doesn’t trigger a fine, a takedown, or a brand crisis.
Content compliance is what stands between a piece of content and the fines, takedowns, or brand damage that come with getting it wrong. For marketing teams specifically, marketing content compliance covers every email, ad, blog post, and social caption: each one has to say what your brand wants it to say, while staying inside legal, regulatory, and accessibility lines that have nothing to do with tone of voice.
Most marketing teams handle this with a patchwork of guideline docs, last-minute legal check-ins, and a hope that nothing slips through.
This guide breaks down what content compliance covers, why it matters more in 2026 than it used to, and a practical workflow for building it into how your team already works.
What is content compliance?
Content compliance means making sure a piece of content meets every standard it needs to before it goes live, not just the brand ones. That includes legal and regulatory requirements (data privacy rules, advertising disclosure laws, sector-specific regulations), brand standards (tone, visual identity, approved claims), intellectual property rules (using licensed assets and properly cleared user-generated content), and accessibility requirements (WCAG standards, alt text, captions).
It’s easy to treat compliance as a brand exercise, checking a piece of copy against a style guide and calling it done. But a perfectly on-brand ad that makes an unsubstantiated claim, or a social post that infringes on someone else’s copyright, is not compliant content, no matter how well it matches the brand voice. Content compliance sits at the intersection of all four areas, and a workflow that only checks one of them, usually the brand one, is only doing part of the job.
What content compliance covers
Digital content compliance covers a lot of ground before a piece of content is published: five different kinds of checks, and a team that only tracks one of them is leaving the other four to chance. Here’s what each one covers.
- Legal and regulatory – data privacy rules, advertising claims and disclosures, and sector-specific regulations that vary by industry and region. For physical products, this extends to packaging and labeling rules too; see our label compliance guide for the specifics. This is where the sharpest legal risk sits, and where the rules change most often. Our marketing compliance guide breaks down the details industry by industry.
- Brand – tone of voice, visual identity, approved claims, and required disclaimers. Most teams already have some process for this one; our brand compliance guide covers what a complete one looks like.
- Intellectual property and licensing – having the rights to every image, font, and piece of music in your content, and proper permission for any user-generated content you reuse. This is the check most teams skip until a takedown notice forces the issue.
- Platform and community standards – the ad, disclosure, and community rules set by Meta, TikTok, YouTube, and other platforms. These rules shift often enough that last year’s sign-off doesn’t guarantee this year’s compliance. Our social media compliance guide covers the specifics.
- Accessibility – meeting WCAG 2.1 AA standards, writing real alt text, and captioning video and audio so content is usable by everyone, not just crawlable by search engines.
Content compliance vs. content moderation vs. content governance
It’s easy to confuse these three, but they’re solving different problems.
- Content compliance asks whether a specific piece of content meets the rules, legal, brand, IP, and accessibility, before it goes out.
- Content moderation is about removing harmful or rule-breaking content that’s already live, usually user-generated, like a comment section or a marketplace listing.
- Content governance is the layer above both: the system, roles, and processes that decide who owns content decisions, how it gets reviewed, and how standards get enforced in the first place.
In practice, a strong content governance model is what makes content compliance possible at scale. Without clear ownership and a defined review process, compliance becomes a person, not a system, and people miss things.
For more on setting that structure up, see our content governance guide.
Fours reasons why content compliance matters
Content compliance was already a lot to manage before AI tools started multiplying how much content your team produces. In 2026, most teams are publishing more content, faster, across more channels, and regulators haven’t gotten any more forgiving about it.
Here’s why it’s worth getting right:
1. Legal and regulatory requirements
Compliance with legal and regulatory standards protects you from real consequences: lawsuits, fines, and regulatory action. Different industries have their own rules, data protection regulations, advertising standards, copyright law, and sector-specific requirements, and getting them wrong doesn’t just cost money. It costs the time your team spends on takedowns, rewrites, and damage control instead of new work.
2. Protecting user safety and well-being
Content compliance protects users from harmful, offensive, or inappropriate content. If your platform allows user-generated content, comments, or reviews, you need policies that catch hate speech, harassment, misinformation, and explicit material before it spreads.
3. Brand reputation and trust
Content and marketing compliance are closely linked to how much people trust your brand. Inaccurate, misleading, or offensive content can undo years of brand-building in a single viral post. Staying compliant is how you protect a reputation that took a long time to build and can disappear fast.
4. Maintaining fairness and equality
Content compliance also covers fairness and non-discrimination, making sure your content treats people equally regardless of race, gender, religion, or sexual orientation. Getting this wrong isn’t just a legal risk, it’s a trust risk that’s much harder to rebuild than a missed deadline.
How to make sure your content is compliant
Building a compliance program is one thing, and marketing compliance covers that ground in full. This is about the narrower, practical question: is the piece of content in front of you right now compliant, and how do you know before you hit publish?
Here’s a six-step check to run on a single asset, whatever process sits around it.
1. Check it against your guidelines
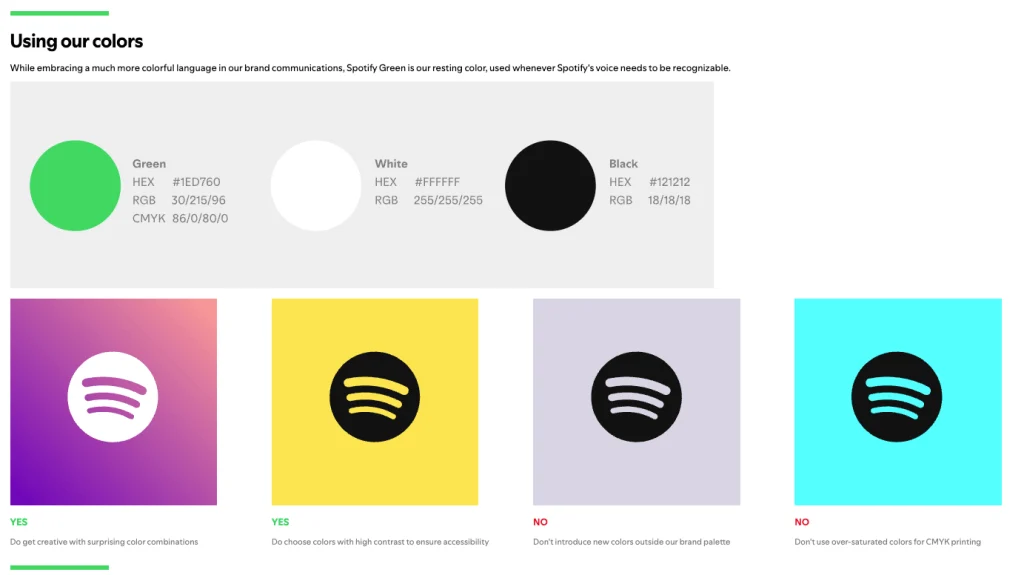
Before anything else, pull up your brand and compliance guidelines, logo usage, color, typography, tone of voice, approved claims, sector-specific rules, and go through the piece line by line. If you’re new to this, this is the reference doc that answers most of your can-I-say-this questions before you have to ask someone.
2. Confirm the brief covered the risk areas
If the piece came from a creative intake form, check that the claims, channel, and any regulatory flags noted at the brief stage are actually reflected in the finished piece. A mismatch here, a claim that got bolder in the final copy than what was briefed, is one of the most common ways non-compliant content slips through.

3. Let an automated check catch the obvious stuff first
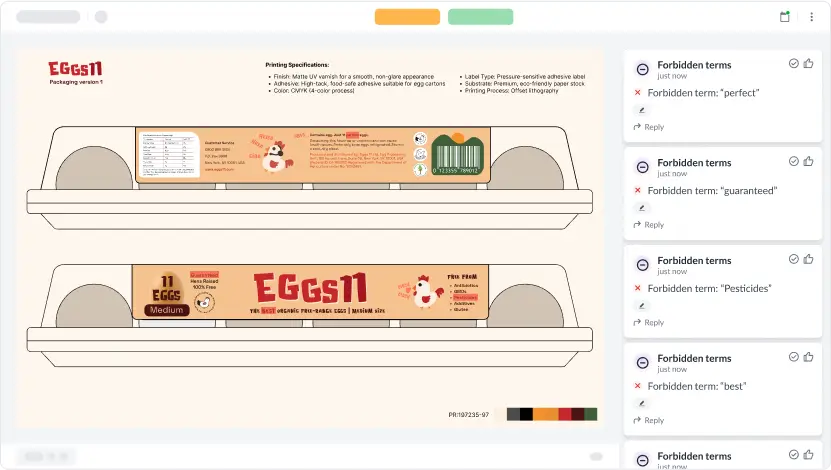
Forbidden words, missing disclaimers, off-brand colors or fonts still need a human’s judgment. What they don’t need is a person combing through the piece to find them first. Filestage’s Review Agents scan the piece against your guidelines before it reaches a reviewer, so the obvious problems get flagged before anyone’s time gets spent on them.
Deliver compliant content with confidence
Set up a consistent and compliant marketing review process with Filestage.
4. Send it to the right reviewers, not just the usual ones
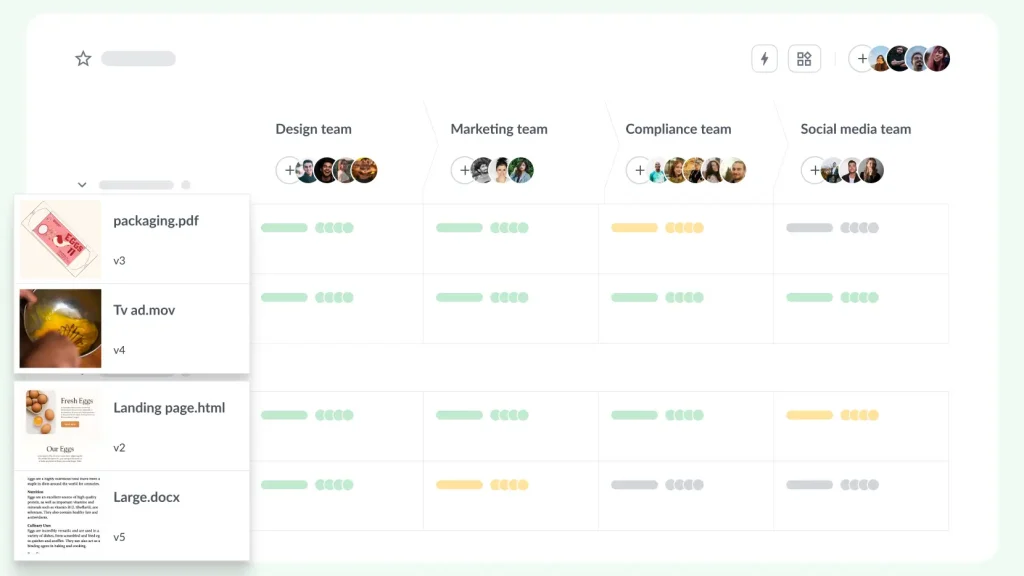
Route the piece through structured content review, and check that the reviewer list actually matches what this specific piece needs. A regulated claim needs legal in the loop. A piece with no legal risk doesn’t need to wait on a legal reviewer who’s going to rubber-stamp it anyway.
5. Confirm the sign-off is actually recorded
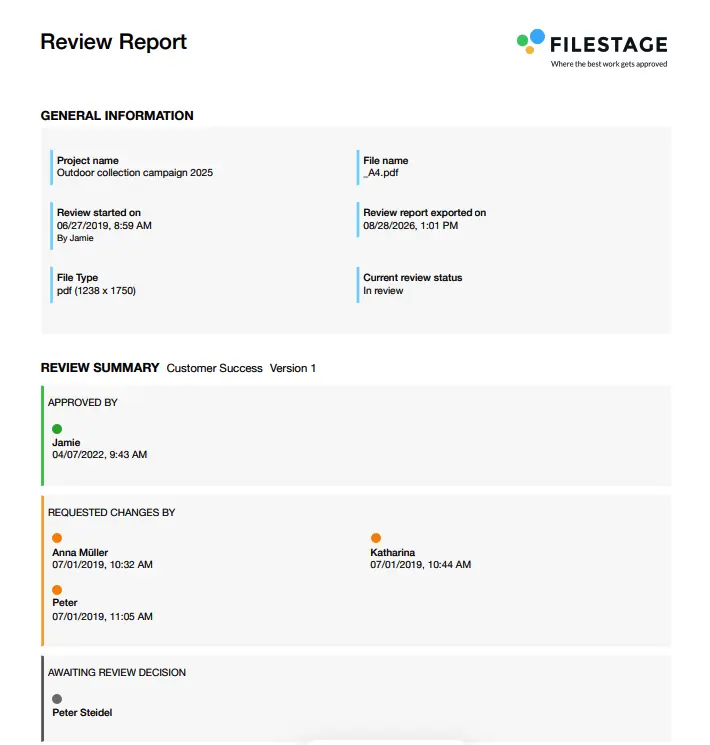
Before you publish, check that the approval trail exists, not just that someone said “looks good” in a comment. Filestage’s review reports log who approved a version and when, automatically, so the record already exists by the time anyone asks for it.
6. Publish, and note when this piece needs a second look
Once it’s live, decide now, not later, when this specific piece should get re-checked. A piece making a time-sensitive claim needs a shorter clock than an evergreen one.
How AI is changing content compliance
AI-written drafts create a specific problem: content that reads as polished and confident even when a claim in it isn’t true. A human writer who’s unsure of a stat usually hedges or flags it. An AI tool usually doesn’t. It states things with the same tone whether the underlying fact checks out or not, which makes AI-generated claims harder to catch on a read-through than a human’s rough draft would be.
That’s a reason to check AI-generated content more closely before it publishes, not less. Building a proper AI content review process means running it through the same guidelines and review steps as anything else, and treating any specific claim, a stat, a comparison, a “studies show,” as unverified until someone’s actually checked it against a source.
An AI review assistant can catch some of this automatically, forbidden terms, missing disclaimers, obvious factual red flags, but the confidence of the writing has nothing to do with whether the claim is true, and that part still needs a person.
Five examples of content compliance settings
When establishing your company’s content compliance guidelines, it’s good to have in mind some of the most prominent examples of such settings.
Here are the five most common examples of content compliance settings:
1. Prohibited content
This setting defines what should never be created, shared, or published: explicit material, hate speech, harassment, illegal activity, or anything that violates applicable law. A common way to enforce this is an advanced content match in Gmail or a similar tool, scanning outbound messages for flagged words or patterns before they ever leave your organization.
2. Unique branding guidelines
These rules keep every piece of content aligned with your brand identity, logo usage, color palette, typography, imagery, and overall visual and textual style, so a customer can recognize your brand’s voice whether they’re reading an email or scrolling a social post. For more on building these out, see our brand compliance guide.
3. Copyright and intellectual property rights
This covers proper attribution, fair use, and licensing for any third-party content you use, images, fonts, music, or stock footage, plus permission for any user-generated content you republish.
4. Advertising and disclosure
If you run ads or sponsored content, this setting covers truthful, accurate representation of your product or service, along with the disclosure requirements that make sponsored content transparent to the people seeing it.
5. Community guidelines
These are the rules of conduct for anyone posting within your platform or community, covering hate speech, harassment, discrimination, and offensive content, and setting the framework for a safe, respectful space.
Tools for ensuring content compliance
Most teams eventually outgrow a guidelines doc and a shared drive. The right software depends on which part of compliance is the bottleneck: general compliance management software for teams juggling legal and regulatory review, brand compliance software for teams whose main risk is off-brand content slipping through, or content governance software for teams that need the system and roles sorted out before the tooling matters.
If your bottleneck is the review step itself, a compliance content review platform combines automated checks with named human sign-off in one workflow.
Filestage covers the review and approval layer that sits underneath all three: structured workflows, Review Agents for automated pre-checks, and a time-stamped record of every decision, so whichever category fits your team, the actual review process doesn’t have to be rebuilt from scratch.
Measure and maintain content compliance over time
Compliance isn’t set-it-and-forget-it. Regulations change, platform rules update without much warning, and content you published two years ago is still live and subject to whatever the rules are today, not whatever they were when you wrote it.
- Set a review cadence – high-risk content, anything with claims, disclosures, or regulated language, gets checked quarterly. Lower-risk content gets an annual pass.
- Track what changed and when – if a regulation or platform policy updates, you need a way to find every piece of content it might affect, not just the new work going forward.
- Keep your guidelines current, not just your content – a guidelines doc that hasn’t been touched in a year is a sign the content governance behind it has gone quiet too.
- Use your audit trail – if you’re already generating a record of approvals and decisions, that same record tells you what’s due for another look and who owns it.
FAQ
Who is responsible for content compliance?
In most organizations, it’s shared: marketing and creative teams own the day-to-day content, legal or compliance teams own the regulatory sign-off, and brand teams own the guidelines everyone’s checking against. The mistake is treating it as one person’s job. Without a shared workflow, compliance becomes whoever remembers to ask, which is exactly how things slip through.
How do you make content compliant?
Set clear guidelines, brief the work properly, run it through review, including legal where needed, and keep a record of who approved what and when. The six-step workflow above covers the full process from brief to publish.
What are examples of content compliance?
Common examples include blocking prohibited content before it’s sent, enforcing brand guidelines across every asset, clearing copyright and licensing on third-party content, disclosing sponsored posts, and setting community guidelines for user-generated content. See the five examples above for the details on each.
Can AI check content compliance?
Yes, to a point. AI-powered checks, like Filestage’s Review Agents, can catch forbidden terms, off-brand language, and missing disclaimers automatically, before a human reviewer opens the file. What AI can’t fully replace is judgment on nuance, context, and situations that haven’t come up before, so automated checks work best as a first pass, not the only one.
How do you make AI-generated content compliant?
Treat AI-generated drafts the same way you’d treat a first draft from a new freelancer: run it through the same guidelines, the same review process, and the same sign-off. Don’t wave it through because a tool wrote it. AI-generated content is especially prone to confidently stated claims that aren’t substantiated, so that’s worth a specific check before it ships.
Final thoughts
Content compliance covers more ground than brand guidelines alone. Legal, regulatory, IP, accessibility, and brand all have to hold up before something goes live. The teams that handle it well build a review and approval workflow that catches problems before publish instead of after.
If you want that workflow built in from brief to sign-off, with an automatic record of every approval along the way, start your free trial of Filestage and see how it fits into what your team already does.